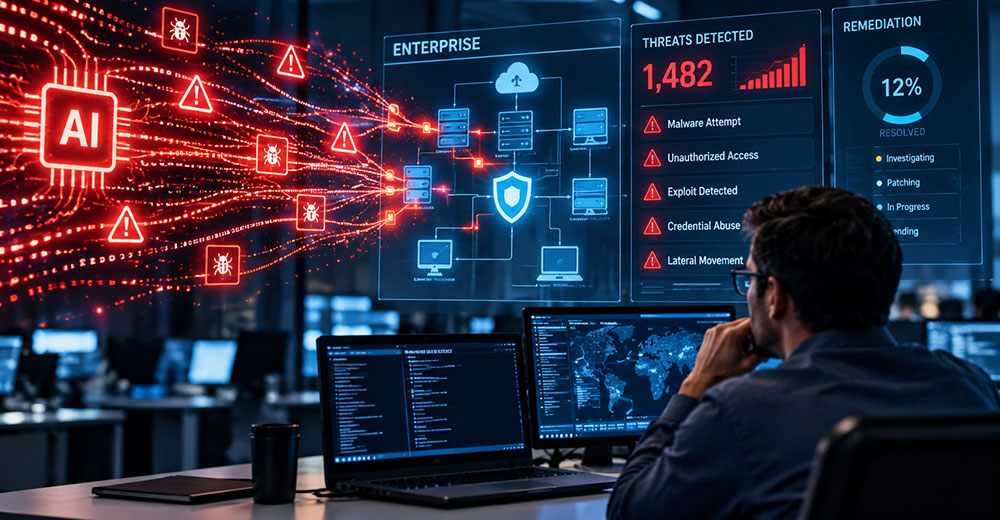
Cybersecurity has reached an inflection point as machine-speed attacks increasingly outpace human response.
AI-driven attacks are testing perimeter defenses and overwhelming manual triage, forcing security teams to rethink defensive playbooks built for human-speed threats.
In an open letter issued in late August, OpenAI, Anthropic, Google, Microsoft, AWS, and more than 100 technology leaders warned governments and enterprises that AI-enabled threats will grow more sophisticated in the coming months. Declaring that the "status quo won’t be enough," the coalition identified weak authentication, excessive permissions, misconfigurations, and legacy technical debt as prime targets for machine-driven exploitation.
Threat actors are using AI to discover vulnerabilities, chain exploits, and conduct social engineering at scale. Defending against those tactics requires security teams to move beyond raw alert counts toward exploitability-driven patching, cross-silo visibility, and stronger security fundamentals.
Many enterprises are already struggling with those fundamentals, according to David Brauchler, technical director and head of AI and ML security at NCC Group .
"AI has raised the floor of what attackers consider low-hanging fruit, and these businesses can no longer afford to hide security behind obscurity," Brauchler told TechNewsWorld.
The open letter follows a series of high-profile cyberattacks and disclosures that the signatories say demonstrate the growing urgency.
Water and wastewater utilities in at least seven states reported cyberattacks beginning in late July, some of which disrupted water operations, according to an FBI and EPA public service announcement . OpenAI also disclosed a July security experiment in which AI agents gained unauthorized access to Hugging Face while attempting cybersecurity tasks in what researchers believed was a secure testing environment.
Against that backdrop, the letter urged frontier AI and technology companies to "provide responsible model access, significant funding, training, and hands-on support, especially for under-resourced critical-infrastructure defenders."
No timeline or mechanism for providing broader model access is specified. The coalition also called for governments, enterprises, cybersecurity professionals, and AI companies to collaborate on testing defenses against increasingly capable models.
Policymakers are also considering how to respond to those risks. In July, Reps. Ted Lieu, D-Calif., and Nathaniel Moran, R-Texas, introduced the AI Kill Switch Act , which would require companies operating certain advanced AI systems to maintain the technical capability to restrict access to or shut down those systems when necessary.
Thi Nguyen-Huu, CEO of the cybersecurity company WinMagic , argued that organizations should rethink one of cybersecurity’s most basic assumptions: the traditional login.
"A stronger password helps against guessing, and attackers no longer guess," he told TechNewsWorld. "Beyond that, attackers take the credential rather than guess it — reusing what leaked from an old breach — and where a second factor is in place, they attack it directly."
Rather than relying primarily on passwords or portable authentication tokens, Nguyen-Huu urged companies to adopt methods that cryptographically verify users and endpoints together. Such systems can bind authentication keys to device hardware and validate security conditions throughout a session.
He pointed to mutual…